Kody Nexov
 Published
Research-backed decision brief - checked 2026-07-24
ISO 27001 and iGaming Provider Security: the decision-ready answer
The correct control set depends on the licensed entity, jurisdiction, product, payment flow, data role, and operating model. Map authoritative obligations to named owners, configurable controls, logs, case evidence, tests, exceptions, and escalation paths.
The assigned US English query igaming provider due diligence was checked on July 24, 2026. The result pattern was used to validate the page intent and question set.
Evidence standard for this decision
Use Yes only when a current source or test explicitly supports the field; Partial when it supports only part of the scope; Not found when the reviewed public sources do not expose it; and Unknown when it has not yet been evaluated. Not found is not evidence that a capability is absent.
| Decision field | Evidence to request | Pass signal | Keep unresolved when |
|---|---|---|---|
| Applicable rule | Current regulator, law, or versioned standard | Scope and effective date are explicit | A supplier badge substitutes for applicability analysis |
| Responsibility | RACI across operator, platform, supplier, and sub-processors | Every decision and evidence artifact has an accountable owner | The contract says both parties cooperate |
| Operating control | Configuration, thresholds, overrides, cases, logs, and retention | A reviewer can reproduce why an action occurred | Only a policy document is supplied |
| Assurance | Test cases, samples, exceptions, remediation, and re-test | Failures have an owner and closure evidence | Certification is treated as proof of every local control |
Questions observed in current demand
The questions below combine the assigned search intent with the evidence gaps found in the current page review.
Which obligations relevant to ISO 27001 and iGaming Provider Security change by jurisdiction, licence, entity, and operating model?
Answer it for a defined operator profile. Compare only like-for-like options, apply one evidence rule, and leave supplier-specific unknowns open until they are closed by current documentation, testing, references, or contract terms.
Question source: archetype - compliance / risk
Which party is responsible, accountable, consulted, and informed for each control?
Start with the applicable entity, market, product, and operating model; then map the authoritative requirement to an owner, configurable control, case record, log, test, exception, and escalation path.
Question source: archetype - compliance / risk
What policy, system, log, test, and case evidence demonstrates that each control operates?
Start with the applicable entity, market, product, and operating model; then map the authoritative requirement to an owner, configurable control, case record, log, test, exception, and escalation path.
Question source: archetype - compliance / risk
Acceptance scenarios
- Trace one normal, one high-risk, and one exception case from input through decision, review, and retained evidence.
- Change a market rule or threshold and verify approval, deployment, monitoring, rollback, and audit history.
- Simulate a regulator or auditor evidence request and measure whether the complete record can be exported.
Source boundary and next evidence
The linked study is the direct research source for this page's topic cluster. It publishes the sample or control set, field definitions, classifications, checked date, primary-source ledger, limitations, and downloadable data. It does not replace jurisdiction-specific legal advice, a supplier proposal, authenticated documentation, a production test, customer references, or a signed contract.
Read the procurement research study or download its CSV dataset.
Decision in brief
Use certification as one input while testing actual security controls and scope. The useful comparison is not the longest feature list. It is the combination of operator fit, verifiable evidence, implementation ownership, measurable service levels, and a workable exit path.
What this guide covers
Use certification as one input while testing actual security controls and scope. It is written for security, compliance, procurement, and ctos. The goal is to turn an early market question into requirements that a buying team can verify during discovery, demos, technical review, commercial negotiation, and implementation planning.
This site does not rank providers. It helps a buying team test claims, structure contracts, and plan implementation and exit.
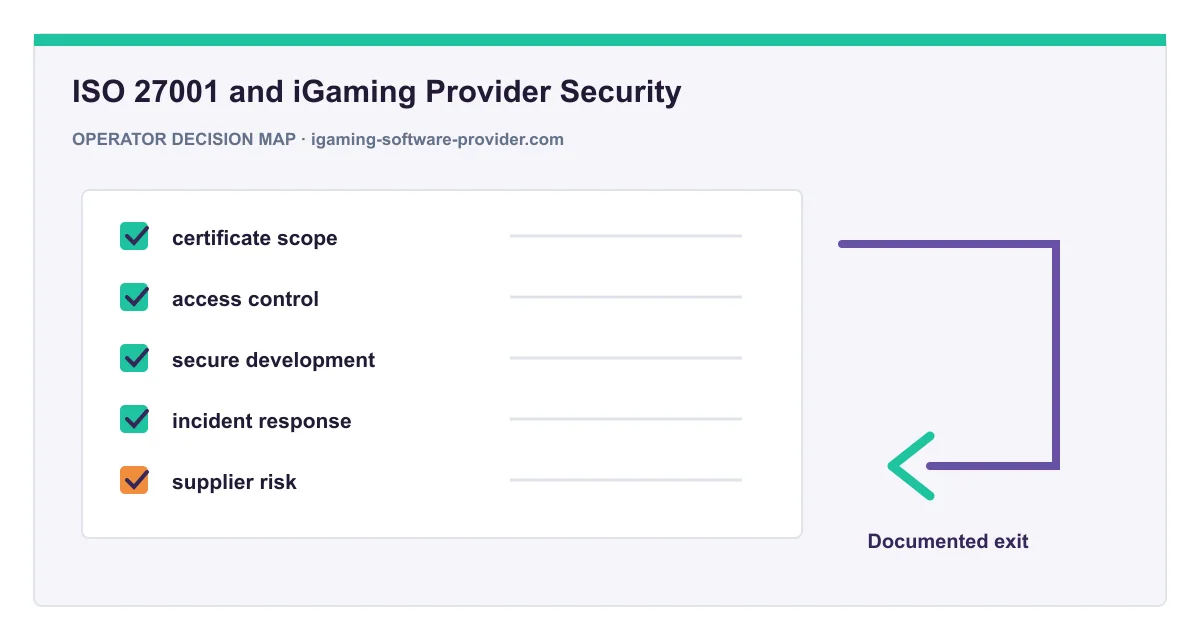
| Area | Evidence to request | Decision owner |
|---|---|---|
| certificate scope | Request current documentation or a live workflow showing how certificate scope is configured, monitored, exported, and supported in production. | Product / operations |
| access control | Request current documentation or a live workflow showing how access control is configured, monitored, exported, and supported in production. | Technology / compliance |
| secure development | Request current documentation or a live workflow showing how secure development is configured, monitored, exported, and supported in production. | Product / operations |
| incident response | Request current documentation or a live workflow showing how incident response is configured, monitored, exported, and supported in production. | Technology / compliance |
| supplier risk | Request current documentation or a live workflow showing how supplier risk is configured, monitored, exported, and supported in production. | Product / operations |
Evaluation checkpoints
1. Confirm ownership and operator control of certificate scope
Define the expected outcome, request proof from the current product, record exceptions, and assign an owner for acceptance.
2. Test integration and data access for access control
Define the expected outcome, request proof from the current product, record exceptions, and assign an owner for acceptance.
3. Review compliance and audit evidence for secure development
Define the expected outcome, request proof from the current product, record exceptions, and assign an owner for acceptance.
4. Put commercial assumptions and exceptions in writing
Define the expected outcome, request proof from the current product, record exceptions, and assign an owner for acceptance.
Implementation sequence
- Define scope and exclusions. Document the operator profile, target market, delivery model, required integrations, and responsibilities that cannot be outsourced.
- Collect comparable evidence. Use the same scenarios and data requests for every candidate. Separate shipped capability from roadmap commitments.
- Run a solution and risk review. Trace critical workflows across product, technology, payments, compliance, operations, finance, and support.
- Convert findings into acceptance criteria. Put dependencies, owners, service levels, data access, timelines, and remedies into the implementation plan and contract.
- Plan controlled go-live and exit. Test degraded modes, reconciliation, incident escalation, rollback, data export, and transition support before production launch.
Questions to put in the RFP
- Show the production workflow and documentation for certificate scope. Which parts are standard, configurable, third-party, or roadmap-only?
- Show the production workflow and documentation for access control. Which parts are standard, configurable, third-party, or roadmap-only?
- Show the production workflow and documentation for secure development. Which parts are standard, configurable, third-party, or roadmap-only?
- Show the production workflow and documentation for incident response. Which parts are standard, configurable, third-party, or roadmap-only?
- Show the production workflow and documentation for supplier risk. Which parts are standard, configurable, third-party, or roadmap-only?
- Which operator teams and external suppliers must participate in implementation, testing, and ongoing operation?
- Which data can the operator access in real time, export in bulk, and retain after termination?
- Provide measurable service levels, escalation paths, maintenance rules, and recent incident examples relevant to this scope.
Red flags
- A broad feature claim without versioned documentation or production evidence.
- An integration dependency with no named owner, test plan, or service level.
- Commercial terms that hide third-party fees, minimums, or transition cost.
Frequently asked questions
What should a buyer verify first when evaluating iso 27001 and igaming provider security?
Start with the operating model and the evidence behind certificate scope. A feature list is not enough: confirm ownership, configuration limits, implementation dependencies, and the exact production version being offered.
Which teams should review iso 27001 and igaming provider security?
Security, compliance, procurement, and CTOs should review the decision together. Product fit, technical feasibility, compliance accountability, commercial terms, and day-to-day operations are connected and should not be approved in isolation.
How should vendor claims be compared?
Use the same requirement matrix, evidence standard, and scoring scale for every vendor. Mark unsupported, roadmap-only, or market-specific claims separately instead of treating them as available capability.
What belongs in the contract or implementation plan?
Document scope, acceptance evidence, dependencies, owners, service levels, data access, change control, and exit support. Any requirement tied to supplier risk should have a named owner and testable acceptance criterion.
Concept map
Related concepts and decision guides
- iGaming Vendor Due Diligence Library
- Work through security, certification, payments, data, lock-in, escrow, and exit evidence before contract approval.
- GLI certification
- Understand what laboratory certification covers and what still requires operator verification.
- KYC AML provider questions
- Test orchestration, evidence, exception handling, and accountability.
- Source Code Escrow for iGaming Software guide
- Decide when escrow is useful and define release, verification, and continuity terms.
- payment provider risk
- Evaluate PSP concentration, settlement, reserves, routing, and continuity.
Evidence layer
Primary references and verification limits
Sources were checked on . They support the standards and verification questions used in this guide. They do not prove a supplier-specific price, market eligibility, implementation result, or private product claim; buyers should request current, versioned evidence for those points.
- iGaming Software Provider - procurement research 2026 Original publisher research. A dated methodology, evidence matrix, primary-source ledger, limitations, and downloadable CSV supporting this page's decision framework.
- OWASP Application Security Verification Standard Open application-security standard. Testable web-application security requirements and procurement-ready verification criteria.
- NIST Cybersecurity Framework 2.0 Government standards body. Cybersecurity governance, risk management, protection, detection, response, and recovery outcomes.
- UK Gambling Commission — Remote gambling and software technical standards Regulator. Remote gambling software controls, security requirements, player-facing technical controls, and jurisdiction-specific verification questions.
- UK Gambling Commission — Testing strategy for remote gambling software Regulator. Testing, release control, audit evidence, change management, independent review, and production assurance questions.