Kody Nexov
 Published
Research for evidence-led software decisions
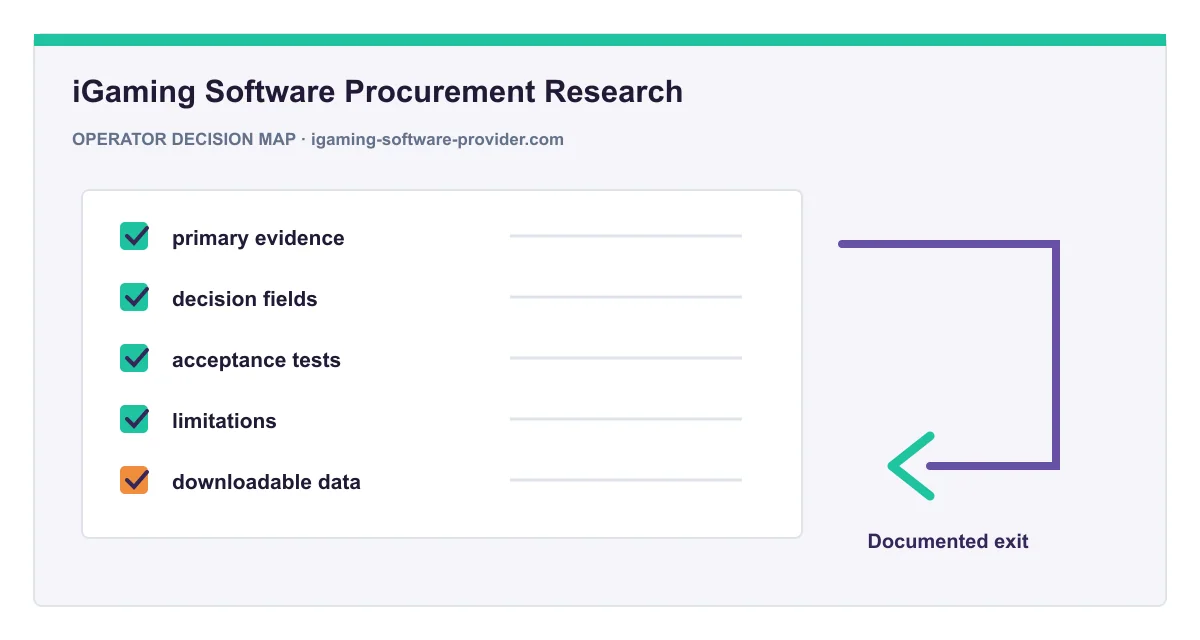
Each study defines a buyer question, freezes the field set, prefers current primary sources, preserves uncertainty, publishes limitations, and provides downloadable data. The work is designed to start an RFP or test plan, not to replace one.
Current studies
iGaming Software Procurement Control Crosswalk 2026
A 2026 iGaming software procurement control crosswalk for contracts, data ownership, security, SDLC, testing, SLA, subprocessors, export, escrow, and exit.
Open the studyPublication standard
- State the operator decision and the unit of analysis.
- Use current supplier, regulator, standards-body, government, or testing sources.
- Separate explicit support, partial support, missing public evidence, and unevaluated fields.
- Publish the checked date, methodology, limitations, source ledger, and CSV.
- Do not infer price, performance, eligibility, compliance, or implementation success from marketing visibility.
Frequently asked questions
Are these pages vendor rankings?
No. They are dated evidence matrices and control crosswalks. They do not score private product quality, price, performance, or customer outcomes.
Why publish the CSV?
The downloadable dataset exposes the field definitions, classifications, source anchors, checked date, and limitations so a buyer can review or adapt the work.
Concept map
Related concepts and decision guides
- How to Choose an iGaming Software Provider comparison
- Create a repeatable provider-selection process based on evidence and operator fit.
- iGaming Software SLA
- Turn availability, support, incident, recovery, and remedy promises into measurable terms.
- iGaming Software Contract Terms guide
- Review scope, acceptance, change control, data, liability, termination, and transition.
- iGaming Vendor Migration implementation guide
- Plan data, integrations, player continuity, certification, and controlled cutover.
- iGaming Software Provider Checklist comparison
- Screen providers before committing to demos and legal review.
Evidence layer
Primary references and verification limits
Sources were checked on . They support the standards and verification questions used in this guide. They do not prove a supplier-specific price, market eligibility, implementation result, or private product claim; buyers should request current, versioned evidence for those points.
- OWASP Application Security Verification Standard Open application-security standard. Testable web-application security requirements and procurement-ready verification criteria.
- NIST Cybersecurity Framework 2.0 Government standards body. Cybersecurity governance, risk management, protection, detection, response, and recovery outcomes.
- AWS Well-Architected — Reliability Pillar Cloud architecture guidance. Availability targets, resilience testing, incident learning, recovery objectives, capacity, and dependency management.
- UK Gambling Commission — Remote gambling and software technical standards Regulator. Remote gambling software controls, security requirements, player-facing technical controls, and jurisdiction-specific verification questions.