Kody Nexov
 Published
Research-backed decision brief - checked 2026-07-24
iGaming Provider Due Diligence: the decision-ready answer
There is no universal best option. Freeze the operator profile, jurisdiction, product boundary, delivery model, retained team, timeline, and risk tolerance; compare like-for-like evidence; and keep public unknowns unresolved until an RFP, demo, test, reference, or contract closes them.
The assigned US English query igaming provider due diligence was checked on July 24, 2026. The result pattern was used to validate the page intent and question set.
Evidence standard for this decision
Use Yes only when a current source or test explicitly supports the field; Partial when it supports only part of the scope; Not found when the reviewed public sources do not expose it; and Unknown when it has not yet been evaluated. Not found is not evidence that a capability is absent.
| Decision field | Evidence to request | Pass signal | Keep unresolved when |
|---|---|---|---|
| Comparison set | One buyer profile and explicit inclusion and exclusion rules | Candidates solve the same layer and operating problem | Platforms, modules, services, and content are mixed |
| Capability evidence | Current official documentation and buyer-owned workflow tests | Yes, Partial, Not found, and Unknown remain distinct | Feature count replaces evidence quality |
| Delivery fit | Responsibility, integration, staffing, market, and implementation map | Retained duties and dependencies are affordable and owned | Turnkey is interpreted as no operator work |
| Commercial and exit | Normalized TCO, SLA, data rights, transition, and remedies | The shortlist remains viable under a high case and an exit case | Only headline price and launch speed are compared |
Questions observed in current demand
The questions below combine the assigned search intent with the evidence gaps found in the current page review.
Which solution types actually solve the buyer need covered by iGaming Provider Due Diligence?
Answer it for a defined operator profile. Compare only like-for-like options, apply one evidence rule, and leave supplier-specific unknowns open until they are closed by current documentation, testing, references, or contract terms.
Question source: archetype - comparison / category
Which candidates belong in the same comparison set, and which solve a different layer?
There is no universal best option. Freeze the operator profile, jurisdiction, product boundary, delivery model, retained team, timeline, and risk tolerance; compare like-for-like evidence; and keep public unknowns unresolved until an RFP, demo, test, reference, or contract closes them. Apply that evidence rule specifically to iGaming Provider Due Diligence and keep unverified product, price, market, and performance claims marked as unknown.
Question source: archetype - comparison / category
Which operator profile, market, product scope, and delivery model changes the shortlist?
Answer it for a defined operator profile. Compare only like-for-like options, apply one evidence rule, and leave supplier-specific unknowns open until they are closed by current documentation, testing, references, or contract terms.
Question source: archetype - comparison / category
Acceptance scenarios
- Score every candidate against the same evidence rule and preserve Not found instead of converting it to No.
- Run the same critical workflow and failure case in each shortlisted product or environment.
- Compare the base, high-volume, delayed-launch, and exit scenario before ranking suppliers.
Source boundary and next evidence
The linked study is the direct research source for this page's topic cluster. It publishes the sample or control set, field definitions, classifications, checked date, primary-source ledger, limitations, and downloadable data. It does not replace jurisdiction-specific legal advice, a supplier proposal, authenticated documentation, a production test, customer references, or a signed contract.
Read the procurement research study or download its CSV dataset.
Due-diligence workplan
Run parallel product, technical, compliance, and commercial reviews
Search results often interpret due diligence as corporate checks or M&A. Software procurement also needs production evidence for the specific product, version, market, implementation team, and contract being proposed.
| Workstream | Core evidence | Stop condition |
|---|---|---|
| Product and operations | Live workflows, permissions, exception handling, roadmap status, comparable references | Critical workflow is unavailable or depends on an uncommitted roadmap item |
| Technology and security | Architecture, SDLC, penetration tests, incidents, recovery tests, API and data controls | No credible owner or evidence for a material security or resilience dependency |
| Compliance | Entity and licence perimeter, certifications, controls, reporting, subcontractors | Proposed supply chain is ineligible or accountability is unresolved |
| Commercial and legal | Complete fees, revenue definitions, SLA, liability, audit, data, IP, termination, transition | Economics or exit terms fail the buyer's approved limits |
Corporate background checks are necessary, but they do not replace product-version and implementation due diligence.
Decision in brief
Verify company, product, security, compliance, delivery, and financial risk. The useful comparison is not the longest feature list. It is the combination of operator fit, verifiable evidence, implementation ownership, measurable service levels, and a workable exit path.
What this guide covers
Verify company, product, security, compliance, delivery, and financial risk. It is written for procurement, investors, legal, security, and executive teams. The goal is to turn an early market question into requirements that a buying team can verify during discovery, demos, technical review, commercial negotiation, and implementation planning.
This site does not rank providers. It helps a buying team test claims, structure contracts, and plan implementation and exit.
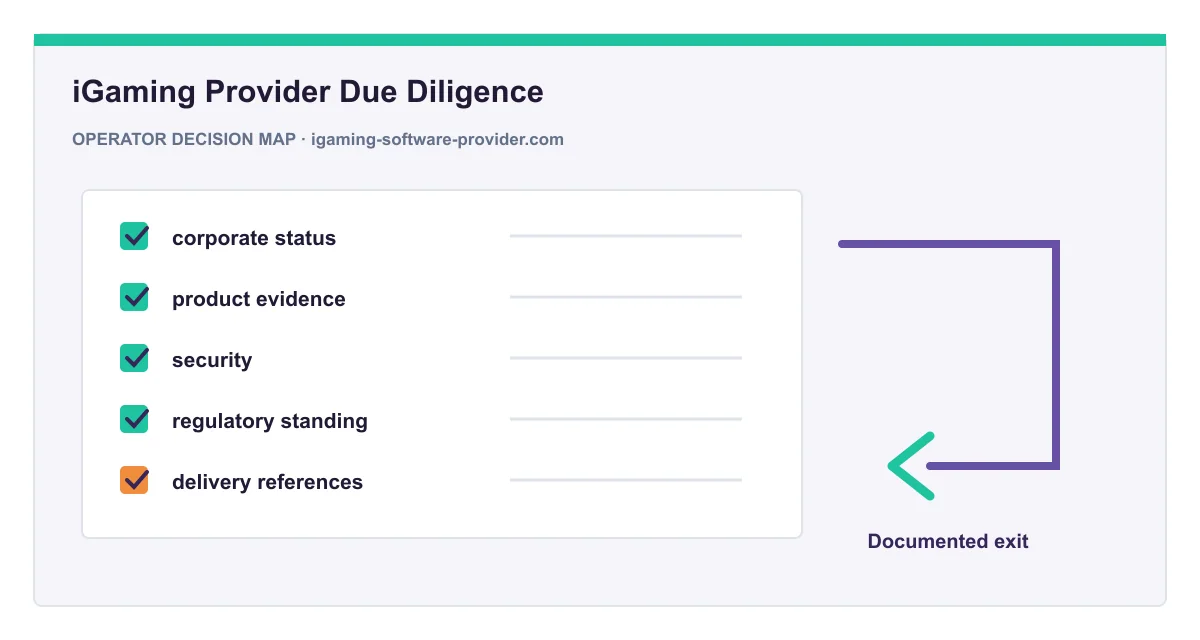
| Area | Evidence to request | Decision owner |
|---|---|---|
| corporate status | Request current documentation or a live workflow showing how corporate status is configured, monitored, exported, and supported in production. | Product / operations |
| product evidence | Request current documentation or a live workflow showing how product evidence is configured, monitored, exported, and supported in production. | Technology / compliance |
| security | Request current documentation or a live workflow showing how security is configured, monitored, exported, and supported in production. | Product / operations |
| regulatory standing | Request current documentation or a live workflow showing how regulatory standing is configured, monitored, exported, and supported in production. | Technology / compliance |
| delivery references | Request current documentation or a live workflow showing how delivery references is configured, monitored, exported, and supported in production. | Product / operations |
Evaluation checkpoints
1. Confirm ownership and operator control of corporate status
Define the expected outcome, request proof from the current product, record exceptions, and assign an owner for acceptance.
2. Test integration and data access for product evidence
Define the expected outcome, request proof from the current product, record exceptions, and assign an owner for acceptance.
3. Review compliance and audit evidence for security
Define the expected outcome, request proof from the current product, record exceptions, and assign an owner for acceptance.
4. Put commercial assumptions and exceptions in writing
Define the expected outcome, request proof from the current product, record exceptions, and assign an owner for acceptance.
Implementation sequence
- Define scope and exclusions. Document the operator profile, target market, delivery model, required integrations, and responsibilities that cannot be outsourced.
- Collect comparable evidence. Use the same scenarios and data requests for every candidate. Separate shipped capability from roadmap commitments.
- Run a solution and risk review. Trace critical workflows across product, technology, payments, compliance, operations, finance, and support.
- Convert findings into acceptance criteria. Put dependencies, owners, service levels, data access, timelines, and remedies into the implementation plan and contract.
- Plan controlled go-live and exit. Test degraded modes, reconciliation, incident escalation, rollback, data export, and transition support before production launch.
Questions to put in the RFP
- Show the production workflow and documentation for corporate status. Which parts are standard, configurable, third-party, or roadmap-only?
- Show the production workflow and documentation for product evidence. Which parts are standard, configurable, third-party, or roadmap-only?
- Show the production workflow and documentation for security. Which parts are standard, configurable, third-party, or roadmap-only?
- Show the production workflow and documentation for regulatory standing. Which parts are standard, configurable, third-party, or roadmap-only?
- Show the production workflow and documentation for delivery references. Which parts are standard, configurable, third-party, or roadmap-only?
- Which operator teams and external suppliers must participate in implementation, testing, and ongoing operation?
- Which data can the operator access in real time, export in bulk, and retain after termination?
- Provide measurable service levels, escalation paths, maintenance rules, and recent incident examples relevant to this scope.
Red flags
- A broad feature claim without versioned documentation or production evidence.
- An integration dependency with no named owner, test plan, or service level.
- Commercial terms that hide third-party fees, minimums, or transition cost.
Frequently asked questions
What should a buyer verify first when evaluating igaming provider due diligence?
Start with the operating model and the evidence behind corporate status. A feature list is not enough: confirm ownership, configuration limits, implementation dependencies, and the exact production version being offered.
Which teams should review igaming provider due diligence?
Procurement, investors, legal, security, and executive teams should review the decision together. Product fit, technical feasibility, compliance accountability, commercial terms, and day-to-day operations are connected and should not be approved in isolation.
How should vendor claims be compared?
Use the same requirement matrix, evidence standard, and scoring scale for every vendor. Mark unsupported, roadmap-only, or market-specific claims separately instead of treating them as available capability.
What belongs in the contract or implementation plan?
Document scope, acceptance evidence, dependencies, owners, service levels, data access, change control, and exit support. Any requirement tied to delivery references should have a named owner and testable acceptance criterion.
Concept map
Related concepts and decision guides
- How to Choose an iGaming Software Provider
- Create a repeatable provider-selection process based on evidence and operator fit.
- iGaming Software Provider Checklist comparison
- Screen providers before committing to demos and legal review.
- iGaming Vendor Migration implementation guide
- Plan data, integrations, player continuity, certification, and controlled cutover.
- iGaming Software Contract Terms guide
- Review scope, acceptance, change control, data, liability, termination, and transition.
- iGaming Software SLA
- Turn availability, support, incident, recovery, and remedy promises into measurable terms.
Evidence layer
Primary references and verification limits
Sources were checked on . They support the standards and verification questions used in this guide. They do not prove a supplier-specific price, market eligibility, implementation result, or private product claim; buyers should request current, versioned evidence for those points.
- iGaming Software Provider - procurement research 2026 Original publisher research. A dated methodology, evidence matrix, primary-source ledger, limitations, and downloadable CSV supporting this page's decision framework.
- OWASP Application Security Verification Standard Open application-security standard. Testable web-application security requirements and procurement-ready verification criteria.
- NIST Cybersecurity Framework 2.0 Government standards body. Cybersecurity governance, risk management, protection, detection, response, and recovery outcomes.
- UK Gambling Commission — Remote gambling and software technical standards Regulator. Remote gambling software controls, security requirements, player-facing technical controls, and jurisdiction-specific verification questions.
- UK Gambling Commission — Testing strategy for remote gambling software Regulator. Testing, release control, audit evidence, change management, independent review, and production assurance questions.